


Beyond NIS2: turning compliance into stronger cybersecurity
 Gergely Lesku
 2026.10.29
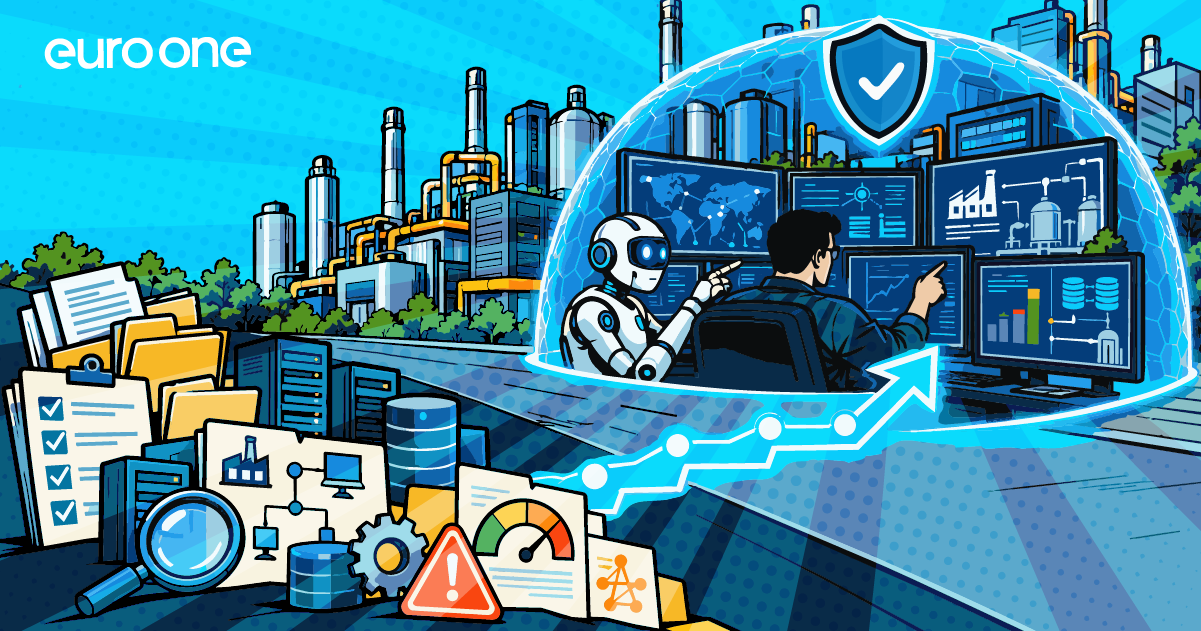
For many businesses, NIS2 preparation demanded considerable time and resources. Yet the process delivered something valuable beyond regulatory compliance: a clearer understanding of critical assets, operational risks, and security gaps. Combined with advances in AI and automation, this knowledge can now help organizations strengthen their cyber defenses.
From regulatory requirements to business value
NIS2 encouraged companies to document their infrastructure, processes, and vulnerabilities. Many now have:
- asset inventories and system documentation;
- business process maps and impact assessments;
- risk evaluations and vulnerability records;
- information on potential cyber threats.
Rather than treating these as static audit documents, organizations can integrate them into everyday security operations to improve risk-based decision-making.
A more complex threat landscape
Ransomware continues to pose a major risk, while AI-powered attack techniques are making cyber threats increasingly sophisticated. Meanwhile, aging infrastructure, interconnected IT systems, and industrial OT environments create additional security challenges.
Security teams must therefore identify and address threats faster, often without additional resources.
Making security information actionable
Digitizing and continuously updating NIS2-related information can transform compliance documentation into operational intelligence. Asset discovery, network monitoring, and OT security technologies help organizations:
- maintain visibility of critical infrastructure;
- identify and prioritize high-risk vulnerabilities;
- improve network segmentation;
- accelerate incident response and limit attack impact.
This approach shifts cybersecurity from periodic assessments toward continuous, risk-based protection.
AI-powered SOC operations
Artificial intelligence can help security teams turn large volumes of alerts into actionable insights. The PULZARIS Analyst Agent supports investigations by connecting related security events, examining historical activity, and considering vulnerability information.
During an investigation, it can identify affected assets, evaluate potential threats, incorporate business criticality, and suggest appropriate response actions.
By automating repetitive analytical tasks, AI enables SOC analysts to focus on complex incidents and critical decisions.
Human expertise remains essential
Despite technological progress, effective cybersecurity still depends on experienced professionals who understand business operations and both IT and OT environments.
The next step after NIS2 is not simply maintaining compliance, but putting the information gathered into practice. By combining existing security knowledge with continuous monitoring, automation, and AI-assisted investigation, organizations can improve resilience and make better use of limited security resources.
Read the full article on our International subsidiary’s website by clicking on the logo: