


How AI is transforming enterprise network security
 Expert of the InfoSec division
 2026.10.16
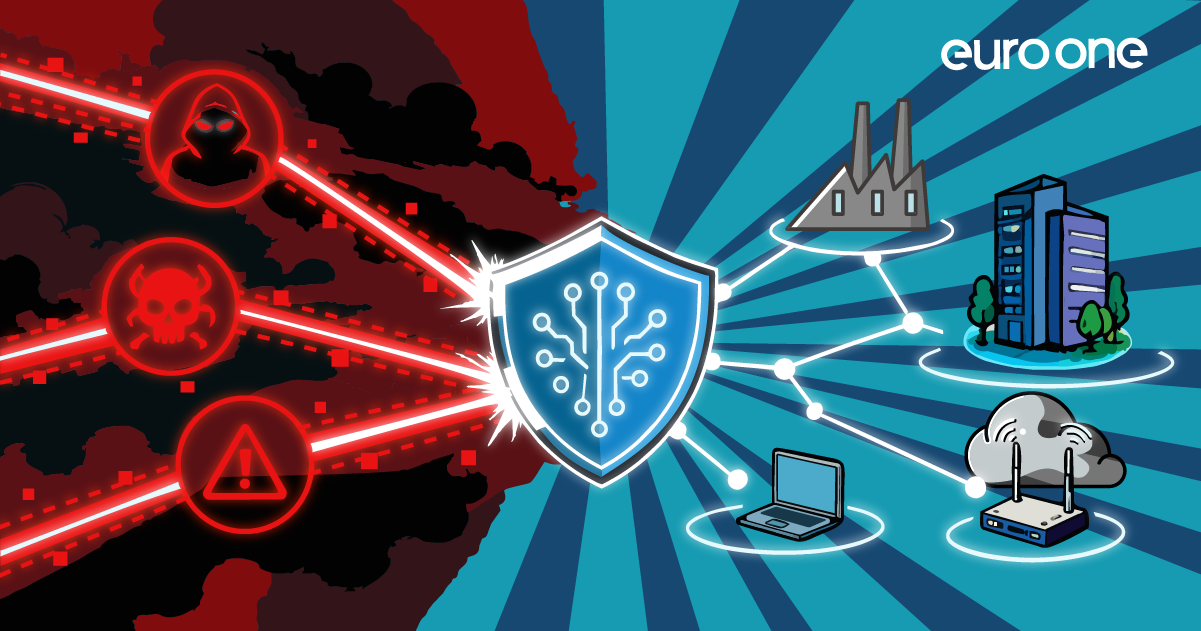
Enterprise networks face a new generation of threats
Corporate networks now extend far beyond traditional data centers. Cloud services, remote employees, IoT devices, operational technology (OT), and SaaS applications create complex environments with numerous potential attack paths.
Meanwhile, cybercriminals are using AI to accelerate vulnerability discovery, automate reconnaissance, and refine their attacks. As conventional security tools struggle to respond quickly enough, AI-powered network protection is becoming essential for business resilience.
Why conventional defenses are no longer enough
Signature-based detection and predefined security rules remain important, but sophisticated attackers increasingly evade them through compromised credentials, disguised network traffic, and rapidly changing techniques.
Security teams must also process enormous amounts of telemetry, often without sufficient visibility into suspicious activity. The priority is shifting from collecting more information to identifying meaningful threats faster.
How AI strengthens network protection
Rather than focusing exclusively on known threats, AI-based solutions examine network behavior to identify unusual patterns and emerging risks.
Their main capabilities include:
Behavioral analysis
Identifying deviations in communication between users, devices, and applications.
Rapid threat detection
Recognizing suspicious connections and lateral movement across network environments.
Intelligent prioritization
Correlating security events to reduce unnecessary alerts and highlight critical incidents.
Automated containment
Blocking harmful traffic or isolating affected systems before attacks spread.
Better visibility means stronger security
Unknown devices, unmanaged applications, and hidden communication paths create significant security gaps, particularly in OT and critical infrastructure environments.
AI-powered monitoring continuously discovers network assets and analyzes their interactions. This helps organizations identify shadow IT, vulnerable systems, unauthorized connections, and potential attack routes.
AI changes the approach to DDoS protection
DDoS attacks are becoming increasingly adaptive as automation enables attackers to modify traffic patterns and sustain disruption.
AI-enhanced defenses help organizations:
- Identify abnormal traffic volumes earlier.
- Distinguish malicious requests from legitimate activity.
- Anticipate attack patterns using historical data.
- Apply targeted mitigation while maintaining service availability.
The objective is not simply to block more traffic, but to stop attacks without unnecessarily interrupting business operations.
A szegmentálás és a „zero trust” megközelítés egyre fontosabbá válik
With increasingly interconnected infrastructures, organizations must prepare for breaches rather than rely entirely on prevention.
Microsegmentation, continuous identity verification, secure remote access, and strict access policies reduce opportunities for attackers to move between systems. These measures are particularly valuable when AI-assisted attacks develop faster than traditional response processes.
Protection cannot wait for patching
New vulnerabilities can be exploited within hours, while deploying software updates may take considerably longer.
To close this exposure window, organizations are adopting virtual patching, AI-assisted intrusion prevention, automated containment, and threat intelligence-based security policies.
The key measure of network security effectiveness is increasingly the time required to establish protection, not merely the time needed to install a patch.
Read the full article on our International subsidiary’s website by clicking on the logo: